One Step LawOne Step Law
  • Data Privacy
    • DPDP Act
      • DPDP Act and Rules
      • Consent Guidelines
      • Data Fiduciary Obligations
      • Data Processor Obligations
      • Data Protection Board of India
      • Cross Border Data Transfer
      • Data Breach Notifications
    • UAE PDPL
    • KSA PDPL
    • Sector-specific privacy (health, ed-tech, fintech)
    DPDP Act
    • DPDP Act
    • DPDP Act and Rules
    • Consent Guidelines
    • Data Fiduciary Obligations
    • Data Processor Obligations
    • Data Protection Board of India
    • Data Breach Notifications
    UAE PDPL
    • UAE PDPL
    • KSA PDPL
    • Sector-specific privacy (health, ed-tech, fintech)
    Latest Posts

    Sector-Specific Data Privacy: Education and the DPDP Act

    6 Min Read

    Sector-Specific Data Privacy: Healthcare and the DPDP Act

    6 Min Read

    KSA PDPL Compliance: Key Obligations for Businesses

    6 Min Read

    KSA PDPL: Understanding Saudi Arabia’s Personal Data Protection Law

    6 Min Read

    UAE PDPL Compliance: What Businesses Need to Know

    7 Min Read

    UAE Personal Data Protection Law: Understanding the UAE PDPL

    7 Min Read
  • Cyber Security
    • CERT-In
      • Advisories and Guidelines
      • Vulnerabilities
      • Whitepapers
    • Data breach notifications
    • Incident response and organizational obligations
    • FinTech (AML/KYC, payment fraud, RBI/SEBI security norms)
      • MEITY Guidelines
      • SEBI Guidelines
      • RBI Guidelines
    DPDP Act
    • CERT-In
    • Advisories and Guidelines
    • Vulnerabilities
    • Whitepapers
    • Data Breach Notifications
    UAE PDPL
    • Incident response and organizational obligations
    • FinTech (AML/KYC, payment fraud, RBI/SEBI security norms)
    • MEITY Guidelines
    • SEBI Guidelines
    • RBI Guidelines
    Latest Posts

    Cybersecurity in FinTech: Understanding RBI Guidelines

    7 Min Read

    Cybersecurity in FinTech: Understanding SEBI Guidelines

    6 Min Read

    Cybersecurity in FinTech: Understanding MeitY Guidelines and the Regulatory Framework

    7 Min Read

    Cybersecurity Incident Response: Organisational Obligations in India

    6 Min Read

    Data Breach Notifications in India: What Businesses Need to Know

    6 Min Read

    CERT-In Whitepapers: Building Awareness and Cybersecurity Resilience

    6 Min Read
  • Cyber Crime News
    • Financial fraud and digital scams
    • Cyber harassment and online abuse
    • Victim remedies and NCRP process
    • IT Act offences and enforcement
    Cyber Crime News
    • Financial fraud and digital scams
    • Cyber harassment and online abuse
    • Victim remedies and NCRP process
    • Victim remedies and NCRP process
    Latest Posts

    Cyber Crime News: IT Act Offences and Enforcement in India

    6 Min Read

    Cyber Crime News: Victim Remedies and the NCRP Process in India

    6 Min Read

    Cyber Crime News: Rising Cyber Harassment and Online Abuse in India

    6 Min Read

    Cyber Crime News: Rising Financial Fraud and Digital Scams in India

    6 Min Read
  • Web3 and AI
    • Blockchain and crypto regulation
    • AI governance and liability
    • Smart contracts and DAOs
    • Metaverse, IoT and other frontier tech
    Web3 and AI
    • Blockchain and crypto regulation
    • AI governance and liability
    • Smart contracts and DAOs
    • Metaverse, IoT and other frontier tech
    Latest Posts

    Web3 and AI: Metaverse, IoT and Other Frontier Technologies

    7 Min Read

    Web3 and AI: Smart Contracts and DAOs — Legal and Regulatory Considerations

    7 Min Read

    Web3 and AI: AI Governance and Liability in India

    7 Min Read

    Web3 and AI: Understanding Blockchain and Crypto Regulation in India

    6 Min Read
  • Case Laws
    • Account Freezing
    • Bail related matters
    • ED & PMLA
    Case Laws
    • Account Freezing
    • Bail Related Matters
    • ED & PMLA
    Latest Posts

    Case Laws on ED and PMLA: Key Judicial Principles

    6 Min Read

    Case Laws on Bail in India: Key Judicial Principles

    7 Min Read

    Case Laws on Account Freezing in India: Understanding the Legal Position

    7 Min Read
  • Scam Stories
One Step LawOne Step Law
  • Data Privacy
    • DPDP Act
    • UAE PDPL
    • KSA PDPL
    • Sector-specific privacy (health, ed-tech, fintech)
  • Cyber Security
    • CERT-In
    • Data breach notifications
    • Incident response and organizational obligations
    • FinTech (AML/KYC, payment fraud, RBI/SEBI security norms)
  • Cyber Crime News
    • Financial fraud and digital scams
    • Cyber harassment and online abuse
    • Victim remedies and NCRP process
    • IT Act offences and enforcement
  • Web3 and AI
    • Blockchain and crypto regulation
    • AI governance and liability
    • Smart contracts and DAOs
    • Metaverse, IoT and other frontier tech
  • Case Laws
    • Account Freezing
    • Bail related matters
    • ED & PMLA
  • Scam Stories
Have an existing account? Sign In
Data PrivacySector-specific privacy (health, ed-tech, fintech)

Sector-Specific Data Privacy: Healthcare and the DPDP Act

Sakshi Srivastava
Last updated: September 9, 2026 7:13 pm
By Sakshi Srivastava
Share
6 Min Read

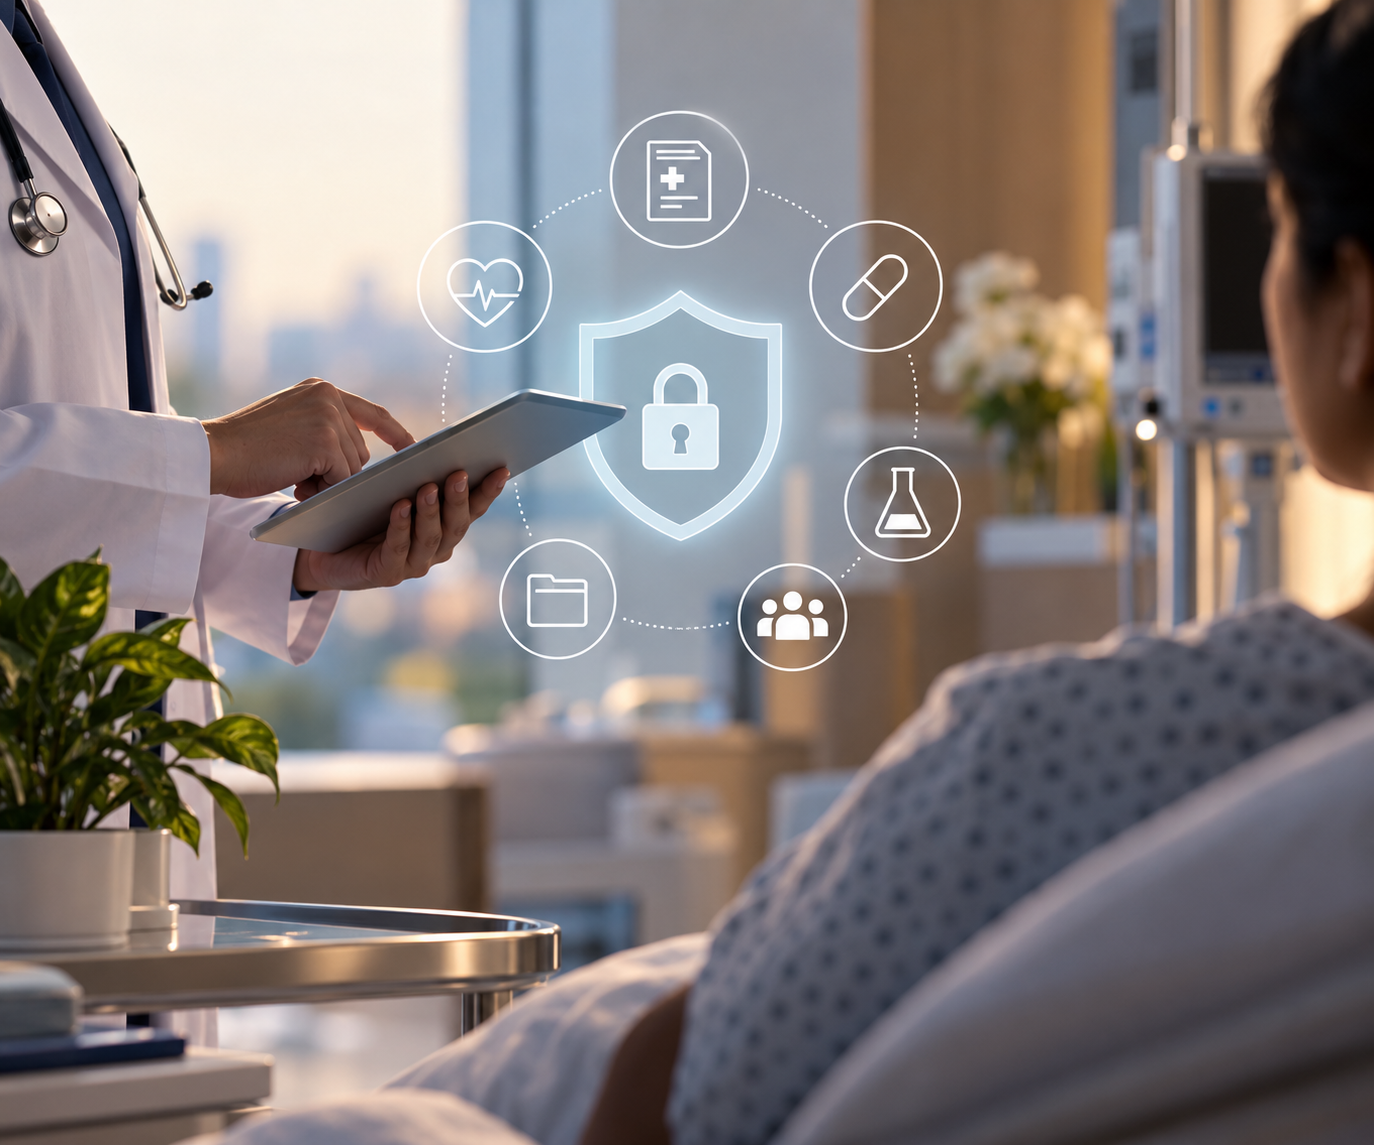
Healthcare is one of the most data-intensive sectors. Hospitals, doctors, diagnostic laboratories, pharmacies, insurers, health-tech companies and digital health platforms routinely collect information such as medical histories, diagnostic reports, prescriptions, identification details, contact information and insurance records. Protecting this information is therefore critical not only from a privacy perspective but also for maintaining patient trust.

Contents
Why Healthcare Data Requires Special AttentionConsent and Healthcare ProcessingDigital Health and ABDMData Security and Breach ManagementManaging Third-Party Healthcare ProvidersConclusion

The Digital Personal Data Protection Act, 2023 (DPDP Act) establishes the general framework governing the processing of digital personal data in India. For healthcare organisations, however, DPDP compliance must be considered alongside other applicable healthcare laws, regulations, contractual obligations and digital health frameworks.

Why Healthcare Data Requires Special Attention

A patient’s medical information can reveal highly personal details about their physical and mental health. A data breach or unauthorised disclosure may result in discrimination, financial harm, reputational damage or other serious consequences.

The DPDP Act does not create a separate statutory category called “sensitive personal data” in the manner of India’s earlier proposed data protection frameworks. Nevertheless, healthcare organisations process personal data that can have significant consequences for individuals and should therefore adopt appropriate safeguards based on the nature and risks of the processing.

The Act requires Data Fiduciaries to implement appropriate technical and organisational measures and reasonable security safeguards to protect personal data from breaches.

Consent and Healthcare Processing

Consent is an important part of the DPDP framework, but healthcare processing cannot always be reduced to a simple consent-based model.

The DPDP Act recognises certain circumstances in which personal data may be processed without consent. These include responding to a medical emergency involving a threat to the life or immediate threat to the health of an individual and providing medical treatment or health services during an epidemic, disease outbreak or other public-health threat.

Healthcare organisations should therefore identify the appropriate legal basis for each processing activity rather than relying on a single general consent mechanism for all patient information.

Digital Health and ABDM

The growth of the Ayushman Bharat Digital Mission (ABDM) has further increased the importance of privacy and consent in India’s digital healthcare ecosystem.

ABDM follows a consent-based approach for sharing health records. The National Health Authority states that ABDM facilitates secure exchange of health information between intended stakeholders after patient consent, while health records continue to be created and stored by the respective healthcare providers.

The ABDM Health Data Management Policy also emphasises privacy and security by design, consent-based processing and protection of personal health data.

This means healthcare organisations participating in digital health ecosystems must carefully manage permissions, access controls and data-sharing arrangements.

Data Security and Breach Management

Hospitals and health-tech companies should implement strong technical and organisational safeguards, including role-based access, authentication, encryption where appropriate, monitoring, secure backups and employee awareness measures.

The DPDP Act also requires Data Fiduciaries to notify the Data Protection Board and affected Data Principals in the prescribed manner when a personal data breach occurs.

Healthcare organisations should therefore maintain a documented incident-response process covering detection, containment, investigation, notification and remediation.

Managing Third-Party Healthcare Providers

Healthcare organisations frequently rely on laboratories, cloud providers, software vendors, insurers, billing platforms and other third-party service providers. Where these entities process personal data on behalf of a healthcare organisation, appropriate contractual controls are essential.

Agreements should address permitted processing, confidentiality, security safeguards, breach reporting, access restrictions, retention and deletion of data.

Conclusion

Healthcare privacy under the DPDP Act requires a risk-based and sector-specific approach. Organisations must understand what patient data they collect, why it is processed, who can access it, where it is stored and when it should be deleted.

With India’s digital healthcare ecosystem expanding rapidly, privacy should be incorporated into healthcare systems from the outset. Strong governance, meaningful consent mechanisms, appropriate security controls and effective breach-response procedures can help healthcare organisations comply with the DPDP framework while protecting one of the most personal forms of information: a patient’s health data.
TAGGED:Data Privacyhealthcaresector-specific privacy
Share This Article
Facebook Whatsapp Whatsapp LinkedIn Copy Link
Previous Article KSA PDPL Compliance: Key Obligations for Businesses
Next Article Sector-Specific Data Privacy: Education and the DPDP Act
Leave a Comment Leave a Comment

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Related Posts

Consent GuidelinesData PrivacyDPDP Act

Consent Guidelines under the DPDP Act, 2023: What Businesses Need to Know

Data PrivacyDPDP ActDPDP Act and Rules

Data Privacy in India: Understanding the DPDP Act, 2023 and DPDP Rules, 2025

Data Fiduciary ObligationsData PrivacyDPDP Act

Data Fiduciary Obligations Under the DPDP Act, 2023

Data PrivacyData Processor ObligationsDPDP Act

Data Processor Obligations Under the DPDP Act, 2023

Data PrivacyData Protection Board of IndiaDPDP Act

Data Protection Board of India Under the DPDP Act, 2023

Cross Border Data TransferData PrivacyDPDP Act

Cross-Border Data Transfer Under the DPDP Act, 2023

FacebookLike
XFollow
YoutubeSubscribe
TelegramFollow

You Might Also Like

Sector-Specific Data Privacy: Education and the DPDP Act

6 Min Read

KSA PDPL Compliance: Key Obligations for Businesses

6 Min Read

KSA PDPL: Understanding Saudi Arabia’s Personal Data Protection Law

6 Min Read

UAE PDPL Compliance: What Businesses Need to Know

7 Min Read
One Step Law
Embark on a flavorful expedition through the rich history of coffee, from the velvety depths of a perfectly brewed espresso to the luxurious foam of a classic cappuccino.
  • Terms of Use
  • Contact Us
  • Privacy Policy
  • About Us
© 2026 One Step Law. All Rights Reserved.
Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?