One Step LawOne Step Law
  • Data Privacy
    • DPDP Act
      • DPDP Act and Rules
      • Consent Guidelines
      • Data Fiduciary Obligations
      • Data Processor Obligations
      • Data Protection Board of India
      • Cross Border Data Transfer
      • Data Breach Notifications
    • UAE PDPL
    • KSA PDPL
    • Sector-specific privacy (health, ed-tech, fintech)
    DPDP Act
    • DPDP Act
    • DPDP Act and Rules
    • Consent Guidelines
    • Data Fiduciary Obligations
    • Data Processor Obligations
    • Data Protection Board of India
    • Data Breach Notifications
    UAE PDPL
    • UAE PDPL
    • KSA PDPL
    • Sector-specific privacy (health, ed-tech, fintech)
    Latest Posts

    Sector-Specific Data Privacy: Education and the DPDP Act

    6 Min Read

    Sector-Specific Data Privacy: Healthcare and the DPDP Act

    6 Min Read

    KSA PDPL Compliance: Key Obligations for Businesses

    6 Min Read

    KSA PDPL: Understanding Saudi Arabia’s Personal Data Protection Law

    6 Min Read

    UAE PDPL Compliance: What Businesses Need to Know

    7 Min Read

    UAE Personal Data Protection Law: Understanding the UAE PDPL

    7 Min Read
  • Cyber Security
    • CERT-In
      • Advisories and Guidelines
      • Vulnerabilities
      • Whitepapers
    • Data breach notifications
    • Incident response and organizational obligations
    • FinTech (AML/KYC, payment fraud, RBI/SEBI security norms)
      • MEITY Guidelines
      • SEBI Guidelines
      • RBI Guidelines
    DPDP Act
    • CERT-In
    • Advisories and Guidelines
    • Vulnerabilities
    • Whitepapers
    • Data Breach Notifications
    UAE PDPL
    • Incident response and organizational obligations
    • FinTech (AML/KYC, payment fraud, RBI/SEBI security norms)
    • MEITY Guidelines
    • SEBI Guidelines
    • RBI Guidelines
    Latest Posts

    Cybersecurity in FinTech: Understanding RBI Guidelines

    7 Min Read

    Cybersecurity in FinTech: Understanding SEBI Guidelines

    6 Min Read

    Cybersecurity in FinTech: Understanding MeitY Guidelines and the Regulatory Framework

    7 Min Read

    Cybersecurity Incident Response: Organisational Obligations in India

    6 Min Read

    Data Breach Notifications in India: What Businesses Need to Know

    6 Min Read

    CERT-In Whitepapers: Building Awareness and Cybersecurity Resilience

    6 Min Read
  • Cyber Crime News
    • Financial fraud and digital scams
    • Cyber harassment and online abuse
    • Victim remedies and NCRP process
    • IT Act offences and enforcement
    Cyber Crime News
    • Financial fraud and digital scams
    • Cyber harassment and online abuse
    • Victim remedies and NCRP process
    • Victim remedies and NCRP process
    Latest Posts

    Cyber Crime News: IT Act Offences and Enforcement in India

    6 Min Read

    Cyber Crime News: Victim Remedies and the NCRP Process in India

    6 Min Read

    Cyber Crime News: Rising Cyber Harassment and Online Abuse in India

    6 Min Read

    Cyber Crime News: Rising Financial Fraud and Digital Scams in India

    6 Min Read
  • Web3 and AI
    • Blockchain and crypto regulation
    • AI governance and liability
    • Smart contracts and DAOs
    • Metaverse, IoT and other frontier tech
    Web3 and AI
    • Blockchain and crypto regulation
    • AI governance and liability
    • Smart contracts and DAOs
    • Metaverse, IoT and other frontier tech
    Latest Posts

    Web3 and AI: Metaverse, IoT and Other Frontier Technologies

    7 Min Read

    Web3 and AI: Smart Contracts and DAOs — Legal and Regulatory Considerations

    7 Min Read

    Web3 and AI: AI Governance and Liability in India

    7 Min Read

    Web3 and AI: Understanding Blockchain and Crypto Regulation in India

    6 Min Read
  • Case Laws
    • Account Freezing
    • Bail related matters
    • ED & PMLA
    Case Laws
    • Account Freezing
    • Bail Related Matters
    • ED & PMLA
    Latest Posts

    Case Laws on ED and PMLA: Key Judicial Principles

    6 Min Read

    Case Laws on Bail in India: Key Judicial Principles

    7 Min Read

    Case Laws on Account Freezing in India: Understanding the Legal Position

    7 Min Read
  • Scam Stories
One Step LawOne Step Law
  • Data Privacy
    • DPDP Act
    • UAE PDPL
    • KSA PDPL
    • Sector-specific privacy (health, ed-tech, fintech)
  • Cyber Security
    • CERT-In
    • Data breach notifications
    • Incident response and organizational obligations
    • FinTech (AML/KYC, payment fraud, RBI/SEBI security norms)
  • Cyber Crime News
    • Financial fraud and digital scams
    • Cyber harassment and online abuse
    • Victim remedies and NCRP process
    • IT Act offences and enforcement
  • Web3 and AI
    • Blockchain and crypto regulation
    • AI governance and liability
    • Smart contracts and DAOs
    • Metaverse, IoT and other frontier tech
  • Case Laws
    • Account Freezing
    • Bail related matters
    • ED & PMLA
  • Scam Stories
Have an existing account? Sign In
Cyber SecurityData breach notifications

Data Breach Notifications in India: What Businesses Need to Know

Sakshi Srivastava
Last updated: September 9, 2026 7:34 pm
By Sakshi Srivastava
Share
6 Min Read

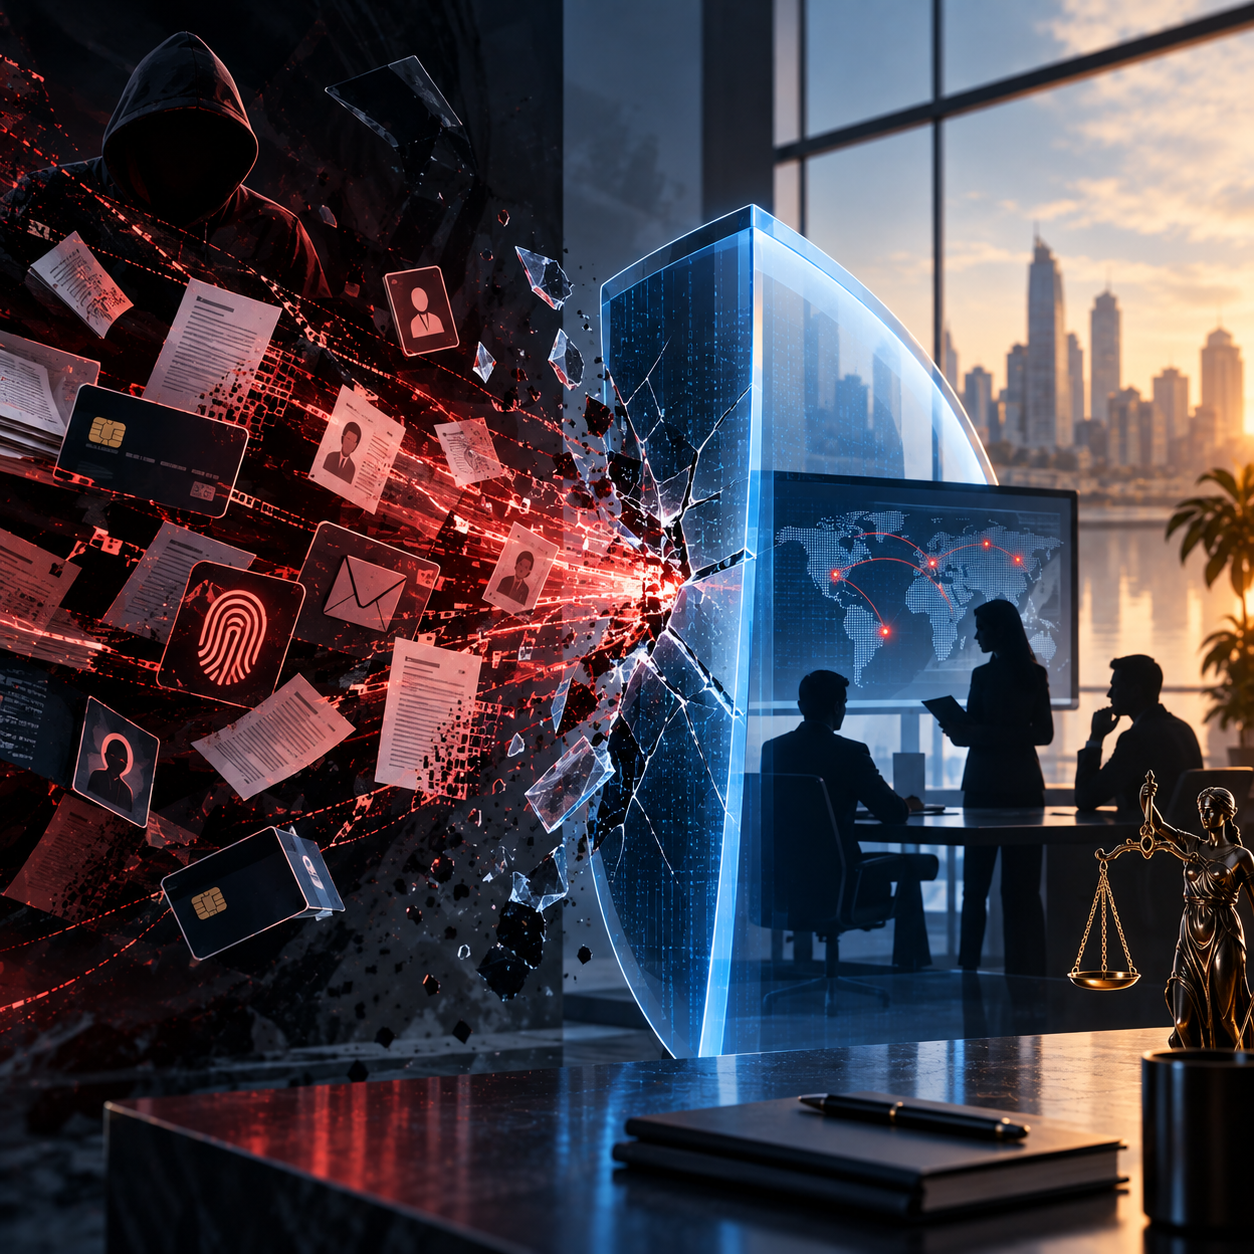
A data breach can expose sensitive customer information, employee records, financial information, credentials and other confidential data. With businesses increasingly dependent on digital systems, responding to a breach is no longer limited to containing the technical problem. Organisations must also understand their regulatory reporting and notification obligations.

Contents
What is a Data Breach?Reporting to CERT-InWhat Information Should Be Reported?Notification to Affected IndividualsPreparing for a Data BreachConclusion

In India, the Indian Computer Emergency Response Team (CERT-In) plays a central role in the reporting and management of cybersecurity incidents. Its Cyber Security Directions issued under Section 70B of the Information Technology Act, 2000 establish reporting requirements for specified cyber incidents, including data breaches and data leaks.

What is a Data Breach?

A data breach occurs when personal or confidential information is accessed, disclosed, altered, lost or obtained without proper authorisation. A breach may result from a successful cyberattack, ransomware, compromised credentials, insider activity, misconfigured cloud storage or even accidental disclosure.

For example, if an employee unintentionally sends a customer database to an unauthorised recipient, the incident may require investigation and appropriate reporting even though there was no deliberate cyberattack.

Reporting to CERT-In

Under the CERT-In Cyber Security Directions, covered entities are required to report specified cyber incidents to CERT-In within six hours of noticing the incident or being brought to notice of it. Data breaches and data leaks are specifically included among the incidents subject to this reporting requirement.

Importantly, an organisation does not necessarily need to wait until every detail of an incident has been established before making the initial report. CERT-In’s FAQs clarify that entities may provide the information available at the time of reporting and submit additional information subsequently within a reasonable period.

This makes early detection and internal escalation particularly important.

What Information Should Be Reported?

CERT-In’s incident-reporting framework contemplates information such as the time of occurrence, affected systems or networks, symptoms observed and relevant technical information, including security measures and actions taken to mitigate the incident.

Organisations should therefore maintain appropriate logs and incident records so that relevant information can be identified quickly when an incident occurs.

Notification to Affected Individuals

Regulatory reporting and communication with affected individuals are separate considerations.

CERT-In advisories concerning data breaches have recommended notifying affected users or customers promptly, explaining the information compromised, measures being taken to address the incident and protective steps that individuals can take.

Depending on the organisation, the nature of the data and the applicable legal framework, additional notification requirements may arise under privacy, sectoral or contractual obligations.

Preparing for a Data Breach

Businesses should not develop their breach-response process after an incident has already occurred. A documented incident response plan should establish who is responsible for identifying, investigating, containing and reporting a breach.

Organisations should also:

  • maintain an updated inventory of critical systems and data;
  • implement appropriate access controls and authentication;
  • continuously monitor security logs;
  • establish an internal escalation mechanism;
  • preserve relevant evidence and logs;
  • maintain contact details for regulatory reporting;
  • conduct periodic incident-response exercises; and
  • review contractual obligations relating to vendors and service providers.

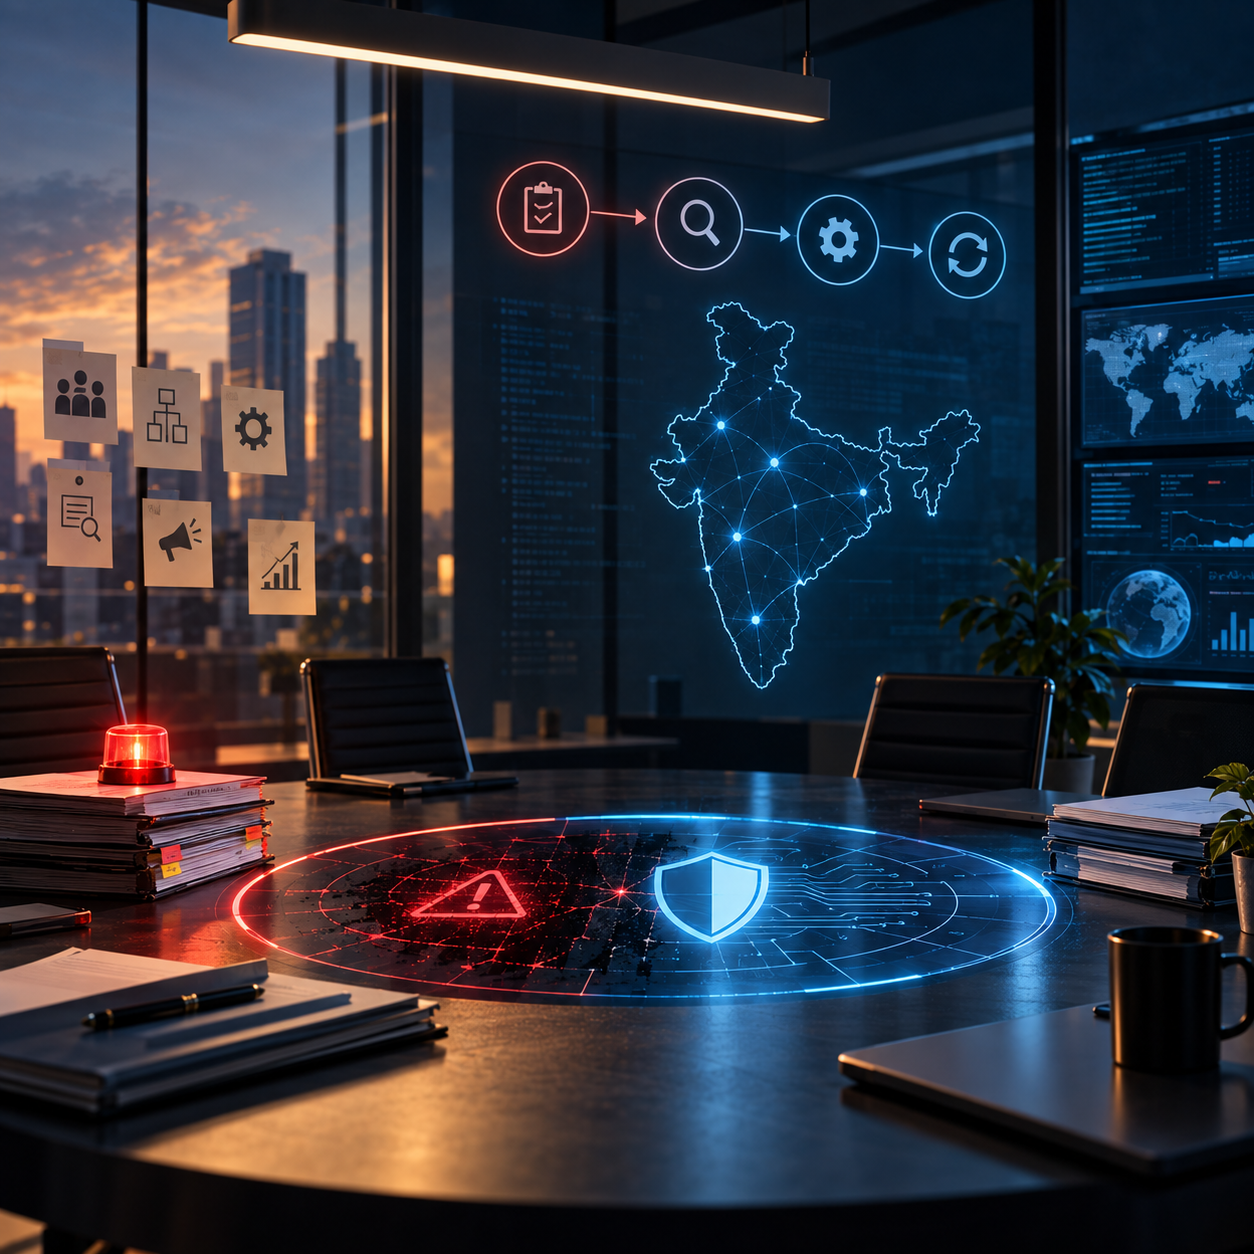
CERT-In’s cybersecurity guidance also emphasises preparation, detection, containment, recovery and lessons learned as important stages of incident management.

Conclusion

A data breach requires both technical and legal response. Organisations must act quickly to contain the incident while simultaneously assessing applicable reporting and notification obligations.

For entities covered by the CERT-In Directions, the six-hour reporting requirement makes preparedness especially important. A well-designed incident-response framework, supported by effective monitoring, clear internal responsibilities and accurate record-keeping, can help businesses respond efficiently when a breach occurs.

Ultimately, effective breach management is not simply about recovering systems. It is about detecting incidents early, protecting affected individuals, complying with reporting obligations and learning from the incident to prevent recurrence.
Share This Article
Facebook Whatsapp Whatsapp LinkedIn Copy Link
Previous Article CERT-In Whitepapers: Building Awareness and Cybersecurity Resilience
Next Article Cybersecurity Incident Response: Organisational Obligations in India
Leave a Comment Leave a Comment

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Related Posts

Consent GuidelinesData PrivacyDPDP Act

Consent Guidelines under the DPDP Act, 2023: What Businesses Need to Know

Data PrivacyDPDP ActDPDP Act and Rules

Data Privacy in India: Understanding the DPDP Act, 2023 and DPDP Rules, 2025

Data Fiduciary ObligationsData PrivacyDPDP Act

Data Fiduciary Obligations Under the DPDP Act, 2023

Data PrivacyData Processor ObligationsDPDP Act

Data Processor Obligations Under the DPDP Act, 2023

Data PrivacyData Protection Board of IndiaDPDP Act

Data Protection Board of India Under the DPDP Act, 2023

Cross Border Data TransferData PrivacyDPDP Act

Cross-Border Data Transfer Under the DPDP Act, 2023

FacebookLike
XFollow
YoutubeSubscribe
TelegramFollow

You Might Also Like

Cybersecurity in FinTech: Understanding RBI Guidelines

7 Min Read

Cybersecurity in FinTech: Understanding SEBI Guidelines

6 Min Read

Cybersecurity in FinTech: Understanding MeitY Guidelines and the Regulatory Framework

7 Min Read

Cybersecurity Incident Response: Organisational Obligations in India

6 Min Read
One Step Law
Embark on a flavorful expedition through the rich history of coffee, from the velvety depths of a perfectly brewed espresso to the luxurious foam of a classic cappuccino.
  • Terms of Use
  • Contact Us
  • Privacy Policy
  • About Us
© 2026 One Step Law. All Rights Reserved.
Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?