One Step LawOne Step Law
  • Data Privacy
    • DPDP Act
      • DPDP Act and Rules
      • Consent Guidelines
      • Data Fiduciary Obligations
      • Data Processor Obligations
      • Data Protection Board of India
      • Cross Border Data Transfer
      • Data Breach Notifications
    • UAE PDPL
    • KSA PDPL
    • Sector-specific privacy (health, ed-tech, fintech)
    DPDP Act
    • DPDP Act
    • DPDP Act and Rules
    • Consent Guidelines
    • Data Fiduciary Obligations
    • Data Processor Obligations
    • Data Protection Board of India
    • Data Breach Notifications
    UAE PDPL
    • UAE PDPL
    • KSA PDPL
    • Sector-specific privacy (health, ed-tech, fintech)
    Latest Posts

    Sector-Specific Data Privacy: Education and the DPDP Act

    6 Min Read

    Sector-Specific Data Privacy: Healthcare and the DPDP Act

    6 Min Read

    KSA PDPL Compliance: Key Obligations for Businesses

    6 Min Read

    KSA PDPL: Understanding Saudi Arabia’s Personal Data Protection Law

    6 Min Read

    UAE PDPL Compliance: What Businesses Need to Know

    7 Min Read

    UAE Personal Data Protection Law: Understanding the UAE PDPL

    7 Min Read
  • Cyber Security
    • CERT-In
      • Advisories and Guidelines
      • Vulnerabilities
      • Whitepapers
    • Data breach notifications
    • Incident response and organizational obligations
    • FinTech (AML/KYC, payment fraud, RBI/SEBI security norms)
      • MEITY Guidelines
      • SEBI Guidelines
      • RBI Guidelines
    DPDP Act
    • CERT-In
    • Advisories and Guidelines
    • Vulnerabilities
    • Whitepapers
    • Data Breach Notifications
    UAE PDPL
    • Incident response and organizational obligations
    • FinTech (AML/KYC, payment fraud, RBI/SEBI security norms)
    • MEITY Guidelines
    • SEBI Guidelines
    • RBI Guidelines
    Latest Posts

    Cybersecurity in FinTech: Understanding RBI Guidelines

    7 Min Read

    Cybersecurity in FinTech: Understanding SEBI Guidelines

    6 Min Read

    Cybersecurity in FinTech: Understanding MeitY Guidelines and the Regulatory Framework

    7 Min Read

    Cybersecurity Incident Response: Organisational Obligations in India

    6 Min Read

    Data Breach Notifications in India: What Businesses Need to Know

    6 Min Read

    CERT-In Whitepapers: Building Awareness and Cybersecurity Resilience

    6 Min Read
  • Cyber Crime News
    • Financial fraud and digital scams
    • Cyber harassment and online abuse
    • Victim remedies and NCRP process
    • IT Act offences and enforcement
    Cyber Crime News
    • Financial fraud and digital scams
    • Cyber harassment and online abuse
    • Victim remedies and NCRP process
    • Victim remedies and NCRP process
    Latest Posts

    Cyber Crime News: IT Act Offences and Enforcement in India

    6 Min Read

    Cyber Crime News: Victim Remedies and the NCRP Process in India

    6 Min Read

    Cyber Crime News: Rising Cyber Harassment and Online Abuse in India

    6 Min Read

    Cyber Crime News: Rising Financial Fraud and Digital Scams in India

    6 Min Read
  • Web3 and AI
    • Blockchain and crypto regulation
    • AI governance and liability
    • Smart contracts and DAOs
    • Metaverse, IoT and other frontier tech
    Web3 and AI
    • Blockchain and crypto regulation
    • AI governance and liability
    • Smart contracts and DAOs
    • Metaverse, IoT and other frontier tech
    Latest Posts

    Web3 and AI: Metaverse, IoT and Other Frontier Technologies

    7 Min Read

    Web3 and AI: Smart Contracts and DAOs — Legal and Regulatory Considerations

    7 Min Read

    Web3 and AI: AI Governance and Liability in India

    7 Min Read

    Web3 and AI: Understanding Blockchain and Crypto Regulation in India

    6 Min Read
  • Case Laws
    • Account Freezing
    • Bail related matters
    • ED & PMLA
    Case Laws
    • Account Freezing
    • Bail Related Matters
    • ED & PMLA
    Latest Posts

    Case Laws on ED and PMLA: Key Judicial Principles

    6 Min Read

    Case Laws on Bail in India: Key Judicial Principles

    7 Min Read

    Case Laws on Account Freezing in India: Understanding the Legal Position

    7 Min Read
  • Scam Stories
One Step LawOne Step Law
  • Data Privacy
    • DPDP Act
    • UAE PDPL
    • KSA PDPL
    • Sector-specific privacy (health, ed-tech, fintech)
  • Cyber Security
    • CERT-In
    • Data breach notifications
    • Incident response and organizational obligations
    • FinTech (AML/KYC, payment fraud, RBI/SEBI security norms)
  • Cyber Crime News
    • Financial fraud and digital scams
    • Cyber harassment and online abuse
    • Victim remedies and NCRP process
    • IT Act offences and enforcement
  • Web3 and AI
    • Blockchain and crypto regulation
    • AI governance and liability
    • Smart contracts and DAOs
    • Metaverse, IoT and other frontier tech
  • Case Laws
    • Account Freezing
    • Bail related matters
    • ED & PMLA
  • Scam Stories
Have an existing account? Sign In
Data Breach NotificationsData PrivacyDPDP Act

Data Breach Notifications Under the DPDP Act, 2023

Sakshi Srivastava
Last updated: September 9, 2026 6:32 pm
By Sakshi Srivastava
Share
7 Min Read

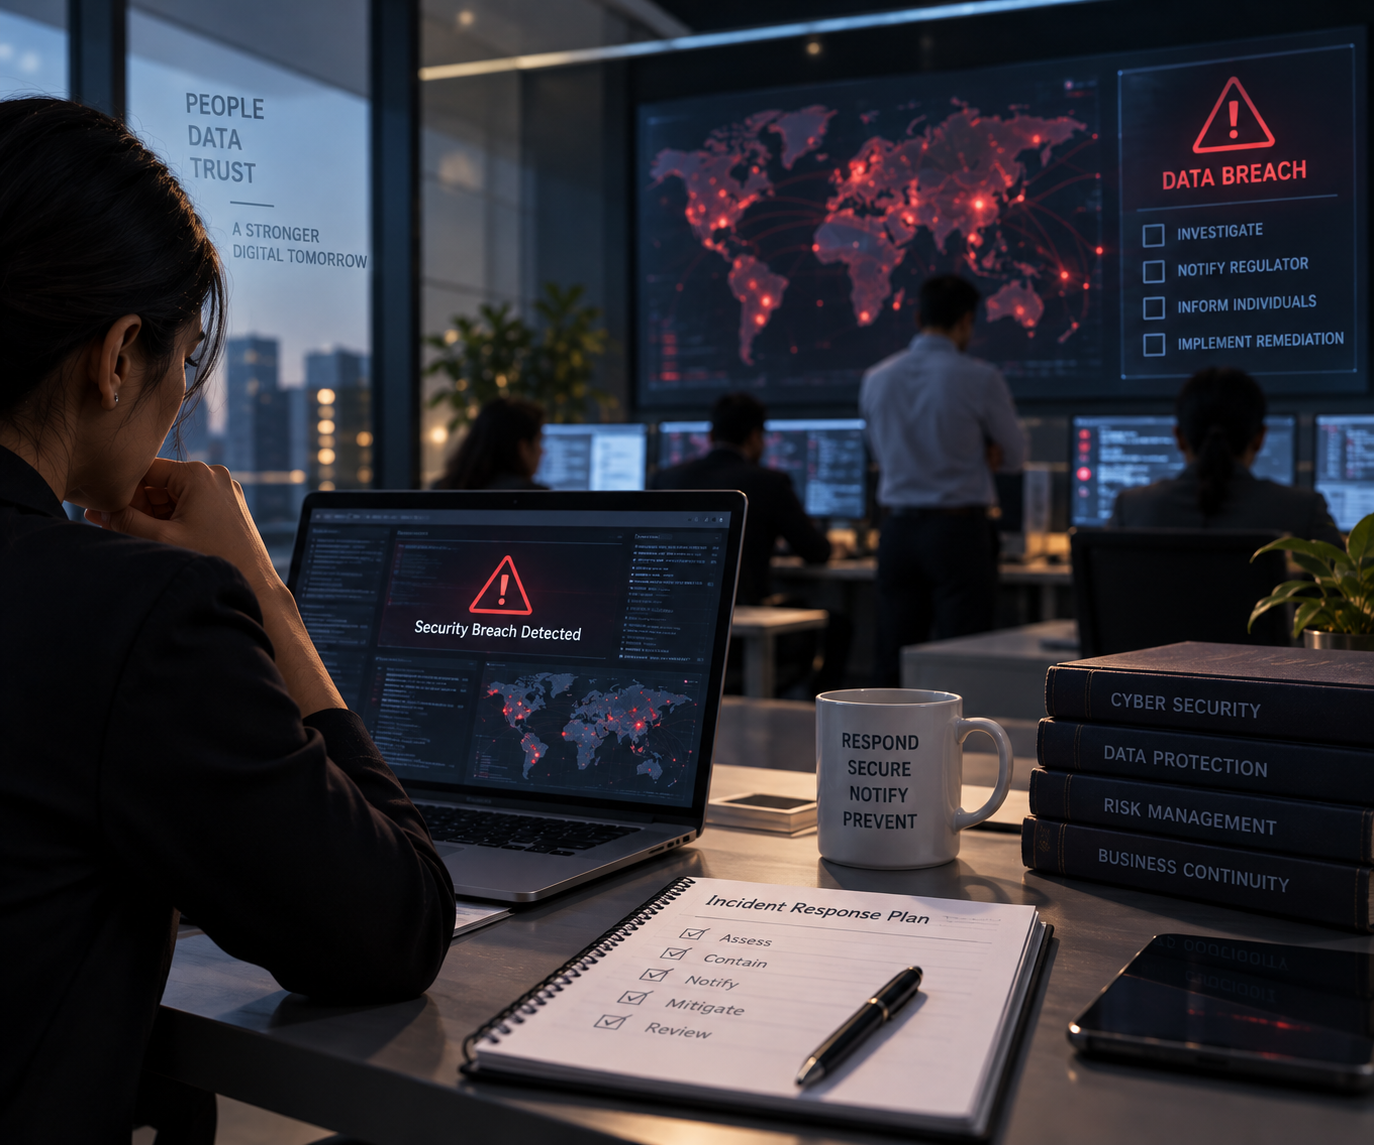
In an increasingly digital economy, organisations collect and process significant volumes of personal data. While businesses may implement security measures to protect this information, data breaches can still occur through cyberattacks, unauthorised access, accidental disclosure, system vulnerabilities or human error. The Digital Personal Data Protection Act, 2023 (DPDP Act) therefore places specific responsibilities on Data Fiduciaries when a personal data breach occurs.

Contents
What is a Personal Data Breach?What Does the DPDP Act Require?What Do the DPDP Rules, 2025 Provide?Why is Timely Notification Important?How Should Businesses Prepare?Conclusion

The Digital Personal Data Protection Rules, 2025 (DPDP Rules) provide greater detail on how such breaches are to be communicated and managed. The Rules were notified in November 2025 and are being brought into force through a phased implementation framework.

What is a Personal Data Breach?

A personal data breach broadly refers to any unauthorised processing of personal data, including accidental or unlawful loss, disclosure, alteration or access that compromises the security of such data.

A breach may involve different forms of incidents—for example, a database being hacked, confidential customer information being accidentally emailed to the wrong recipient, or an unauthorised person gaining access to an organisation’s systems.

The DPDP framework treats breach management as an important part of a Data Fiduciary’s overall responsibility for protecting personal data.

What Does the DPDP Act Require?

Under Section 8(6) of the DPDP Act, where a personal data breach occurs, the Data Fiduciary is required to intimate the Data Protection Board of India and each affected Data Principal in the prescribed manner and form. The Board may, upon receiving information regarding a breach, direct urgent remedial or mitigation measures and inquire into the breach.

This means that responding to a breach is not limited to internally containing the incident. The organisation must also consider its regulatory and communication obligations.

What Do the DPDP Rules, 2025 Provide?

Rule 7 of the DPDP Rules, 2025 provides a more detailed framework for breach notifications.

When a Data Fiduciary becomes aware of a personal data breach, it must promptly inform affected Data Principals. The communication should be clear and understandable and should explain important information, including the nature, extent and timing of the breach and its likely consequences for the affected individual.

The notification should also identify measures taken by the organisation to mitigate the effects of the breach and provide practical recommendations to help affected individuals protect themselves. Contact details of a person who can respond to questions relating to the breach must also be provided.

The Data Fiduciary must additionally inform the Data Protection Board without delay. Within 72 hours, or such longer period as may be allowed by the Board, it must provide detailed information regarding the breach, including the circumstances leading to it, the measures taken to mitigate its effects, remedial measures adopted to prevent recurrence and details of notifications issued to affected Data Principals.

Why is Timely Notification Important?

A data breach can expose individuals to risks such as identity theft, financial fraud, phishing and other forms of misuse. Prompt notification allows affected individuals to take protective measures at an early stage.

For businesses, timely reporting also forms part of regulatory compliance. Failure to maintain appropriate security safeguards or comply with breach-related obligations can attract significant penalties under the DPDP framework.

How Should Businesses Prepare?

Organisations should have a documented data breach response plan covering detection, internal escalation, investigation, containment, regulatory notification and communication with affected individuals.

Businesses should also maintain appropriate security safeguards, monitor systems for unauthorised access, maintain relevant logs and ensure that Data Processor contracts contain appropriate security requirements.

Conclusion

The DPDP Act and Rules make data breach management an important element of privacy governance. Organisations must be prepared not only to prevent breaches but also to respond quickly and transparently when incidents occur.

Effective breach preparedness therefore requires a combination of technical safeguards, internal response procedures, contractual controls and timely communication. As the DPDP framework moves through its phased implementation, organisations should use this period to strengthen their incident-response mechanisms and build a culture of responsible data protection.
TAGGED:Data Breach NotificationsData PrivacyDPDP Act
Share This Article
Facebook Whatsapp Whatsapp LinkedIn Copy Link
Previous Article Cross-Border Data Transfer Under the DPDP Act, 2023
Next Article UAE Personal Data Protection Law: Understanding the UAE PDPL
Leave a Comment Leave a Comment

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Related Posts

Consent GuidelinesData PrivacyDPDP Act

Consent Guidelines under the DPDP Act, 2023: What Businesses Need to Know

Data PrivacyDPDP ActDPDP Act and Rules

Data Privacy in India: Understanding the DPDP Act, 2023 and DPDP Rules, 2025

Data Fiduciary ObligationsData PrivacyDPDP Act

Data Fiduciary Obligations Under the DPDP Act, 2023

Data PrivacyData Processor ObligationsDPDP Act

Data Processor Obligations Under the DPDP Act, 2023

Data PrivacyData Protection Board of IndiaDPDP Act

Data Protection Board of India Under the DPDP Act, 2023

Cross Border Data TransferData PrivacyDPDP Act

Cross-Border Data Transfer Under the DPDP Act, 2023

FacebookLike
XFollow
YoutubeSubscribe
TelegramFollow

You Might Also Like

Sector-Specific Data Privacy: Education and the DPDP Act

6 Min Read

Sector-Specific Data Privacy: Healthcare and the DPDP Act

6 Min Read

KSA PDPL Compliance: Key Obligations for Businesses

6 Min Read

KSA PDPL: Understanding Saudi Arabia’s Personal Data Protection Law

6 Min Read
One Step Law
Embark on a flavorful expedition through the rich history of coffee, from the velvety depths of a perfectly brewed espresso to the luxurious foam of a classic cappuccino.
  • Terms of Use
  • Contact Us
  • Privacy Policy
  • About Us
© 2026 One Step Law. All Rights Reserved.
Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?